Composite rule support for Outbreak Rules
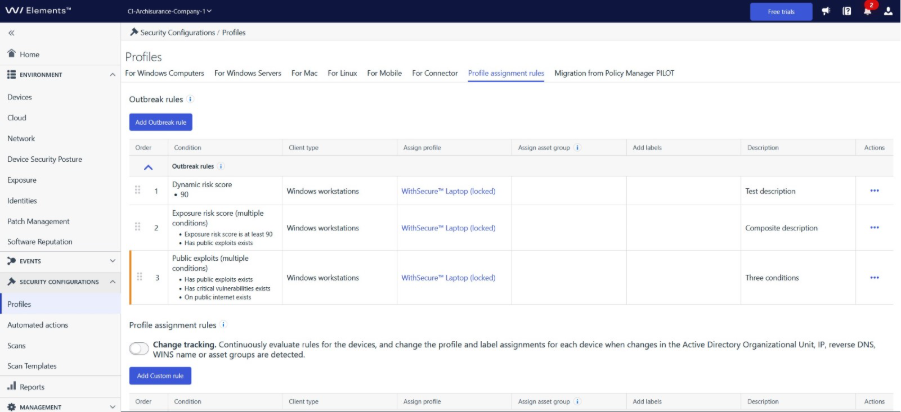
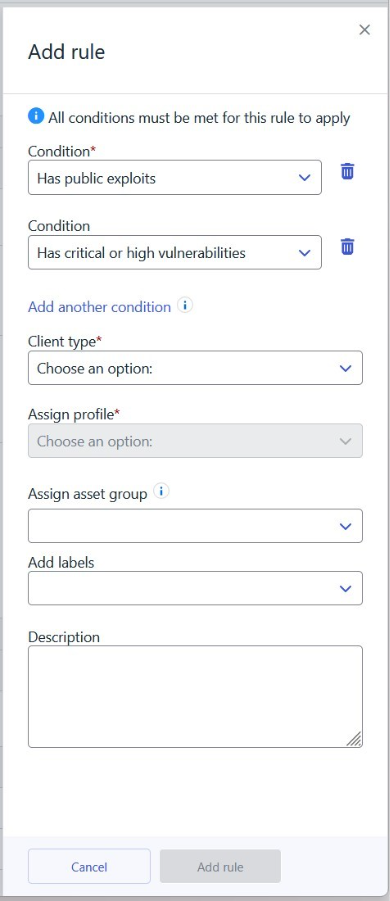
We are now adding support for composite rules to the existing Outbreak Rules functionality, along with new conditions. These will allow for an outbreak rule to apply when two or more conditions are met, rather than a single condition in isolation.
We expect this functionality to be available for all customers on 2026-04-23.
How it works?
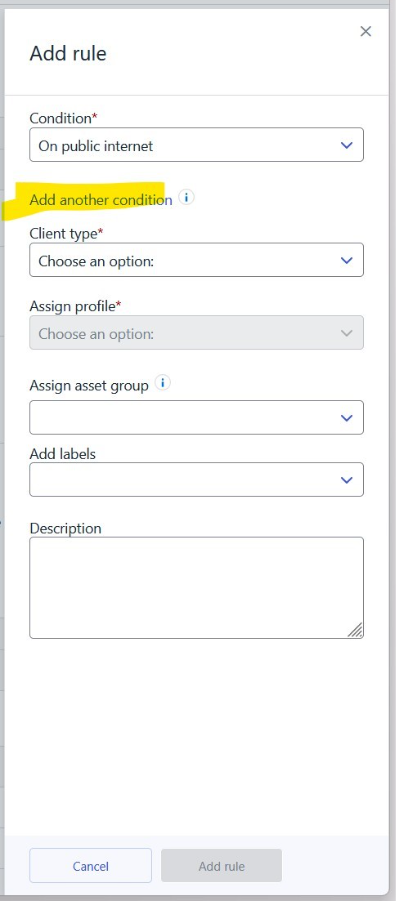
As an example, a rule could be added that would trigger if a device was both on the public internet and had critical vulnerabilities.
The new outbreak control conditions are as follows:
- Has public exploits
- Has critical vulnerabilities
- Has critical or high vulnerabilities
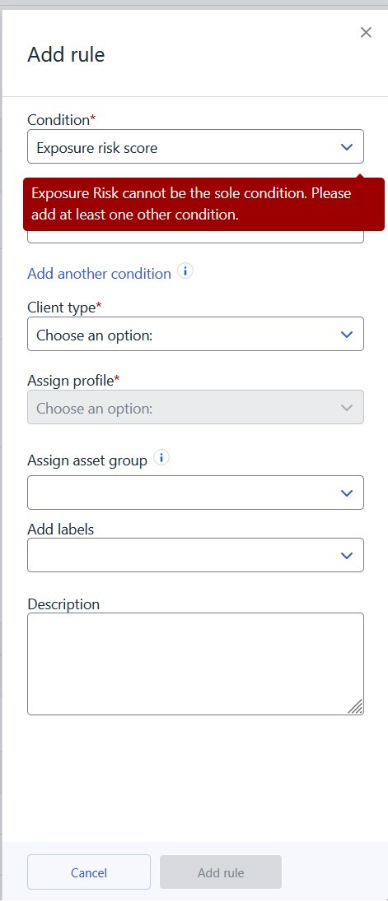
- Exposure Risk score
Additional notes
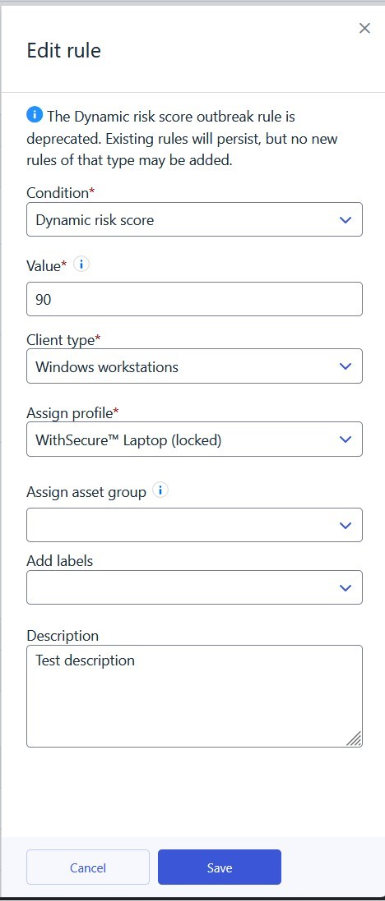
The existing Dynamic Risk score condition is being deprecated in favour of the Exposure Risk score. Existing rules will not be modified in this process and will work as before, but it will no longer be possible to assign Dynamic Risk score conditions to new rules. It will still be possible to edit existing rules.
In some circumstances it may be difficult to reduce the Exposure Risk score; for this reason, that condition will be restricted to composite rules initially.