
-
Controlled Updates for WithSecure Elements agents
Read more
Dear community,
We are introducing Controlled Updates for WithSecure Elements agents, giving you the ability to align agent updates with your own change and maintenance windows rather than receiving them as soon as they are published.
What is changing?
Until now, Elements agents have updated automatically as new versions became available. You can now choose the update mode per profile:
- Automatic Updates — devices receive new agent versions as they are released. This remains the default, and nothing changes for profiles you leave as they are.
- Controlled Updates — devices stay on an assigned release group until you upgrade them, or until that group expires.
Because the setting is applied per profile, you can mix modes across your estate — for example, keeping workstations on Automatic Updates while applying Controlled Updates to servers.
What to know before you start
- Security intelligence updates are not affected by this setting. They continue to be delivered to all devices regardless of the update mode you choose.
- This is not a way to postpone updates indefinitely. Devices are brought up to date automatically once their assigned release group expires.
- Controlled Updates is not supported alongside the Elements Connector.
- Available for Windows, macOS, and Linux Elements agents.
For release group schedules, configuration steps, and how to assign devices, see Controlled Updates in the user guide.
We believe this improvement will give administrators working under strict change control the predictability they need, without weakening the protection on the devices themselves.
-
Agent for Mobile – 2026-08-17 Update
Read more
An update to the WithSecure Elements Mobile Protection app for iOS (26.7.12397) has been released on the 17 August 2026 with phased rollout (1 week).
It includes the following new features and improvements:
- Content Filter feature:
- The app now supports Content Filter as an alternative to VPN-based traffic inspection on supervised, MDM-managed iOS and iPadOS devices
- The inspection mode can now be selected on the device or configured in the WithSecure Elements Endpoint Protection portal
- The app now automatically switches to VPN-based inspection if Content Filter cannot be activated
- Content Filter allows Mobile Protection to operate alongside other VPN providers
Note: Content Filter requires an appropriate Web Content Filter configuration profile to be deployed to the device through MDM.
- Content Filter feature:
-
Collaboration Protection – 2026-07-31 Update
Read more
Action Required: Existing EWS‑Quarantined Items
Following the announcement about the Collaboration Protection Exchange protection transition to Microsoft Graph API, action may be required by administrators.
What’s changing
Items previously quarantined via EWS — particularly Calendar events, Contacts, Tasks, Notes and Sticky notes — will no longer be accessible via the Graph API once the migration is complete. Due to this limitation, action is needed for items that were previously quarantined via EWS.
What you need to do
Administrators must verify if they would like to release or delete any of the existing EWS-quarantined items, which will no longer be accessible via Graph API, no later than August 31, 2026. Any items left unreleased by this date will be automatically deleted by ECP on September 15, 2026.
How to identify affected items
Items requiring action can be identified in the Collaboration Protection portal, on the Quarantine page, in two ways:
- Check the item type via detection details – Select “View detection” on the quarantined item and verify whether the Item type is one of: Appointment, Contact, Contact group, Post item, or Task.
- Use the new Item type filter – Apply the filter: Exchange → Item type: Calendar event, Contact, or Other.
Either method will help you identify items that require verification and possible action before the deadlines above.
-
Agent for Mac – 2026-07-16 Update
Read more
WithSecure Elements Agent for Mac 26.3 was released to general availability (GA) on 16 July 2026.
This release includes the following bug fixes:
- Fixed an issue where XFence could incorrectly block properly signed third-party applications.
- Fixed an issue where remote software update installation could occasionally fail.
- Fixed a crash in the
wssettingsdcomponent. - Fixed an issue where Full Disk Access permission could be repeatedly requested even after being granted on macOS 26 Tahoe.
- Fixed an issue where the “Send full status” remote action did not return updated status.
The installer can be downloaded from:
https://download.withsecure.com/PSB/latest/ElementsAgentInstaller.mpkg
WithSecure Elements Agent for Mac 26.3 supports the following macOS versions:
- macOS 26 Tahoe
- macOS 15 Sequoia
- macOS 14 Sonoma
-
Agent for Mac – 2026-07-10 Update
Read more
WithSecure Elements Agent for Mac 26.3 has been released to our early access customers. General availability will follow within the next couple of weeks.
This release includes the following bug fixes:
- Fixed an issue where XFence could incorrectly block properly signed third-party applications.
- Fixed an issue where remote software update installation could occasionally fail.
- Fixed a crash in the
wssettingsdcomponent. - Fixed an issue where Full Disk Access permission could be repeatedly requested even after being granted on macOS 26 Tahoe.
- Fixed an issue where the “Send full status” remote action did not return updated status.
Installer can be downloaded from:
https://download.withsecure.com/PSB/latest/ElementsAgentInstaller_56020.mpkg
WithSecure Elements Agent for Mac 26.3 supports the following macOS versions:
- macOS 26 Tahoe
- macOS 15 Sequoia
- macOS 14 Sonoma
-
Agent for Mobile – 2026-07-01 Update
Read more
An update to the WithSecure Elements Mobile Protection app for Android (26.5.23651) has been completed 1 July 2026. It will be released as a phased rollout over the next seven days.
It includes the following bug fixes:
- General stability and performance improvements to reduce crashes and cases where the app could stop responding
- The app no longer shows multiple notifications for a single blocked website
- Allowed websites now load correctly when “Block everything except allowed sites” is enabled
- The allowed-sites list now matches website addresses by host, so lookalike domains are no longer treated as allowed
- User profile information (first name, last name, alias) is no longer cleared on MDM-managed devices after a policy refresh
- The copyright year shown in About is now correct
-
Endpoint Security (formerly Endpoint Detection & Response) — 2026-06-29 Update
Read more
Dear community,
We are expanding the Automated actions feature in Elements EDR to help partners respond to endpoint threats faster and at scale. With this update, you can now create automated rules that trigger six new EDR response actions whenever a Broad Context Detection (BCD) is created or updated to a medium, high, or severe risk level.
What is changing?
Automated Actions for endpoint rules already supported Device Isolation as an automated response. We are now adding six new response actions, giving you greater flexibility to automate incident response across your customer organisations.
With this update, six new response actions are available for automation:
- Retrieve files – collects files from endpoints based on path patterns,
- Enumerate services – lists all installed services on Windows endpoints,
- Retrieve browser artefacts – collects browser history and data from major browsers,
- Netstat – retrieves network connection information,
- Enumerate scheduled tasks – lists Windows scheduled tasks,
- Enumerate processes – lists all running processes.
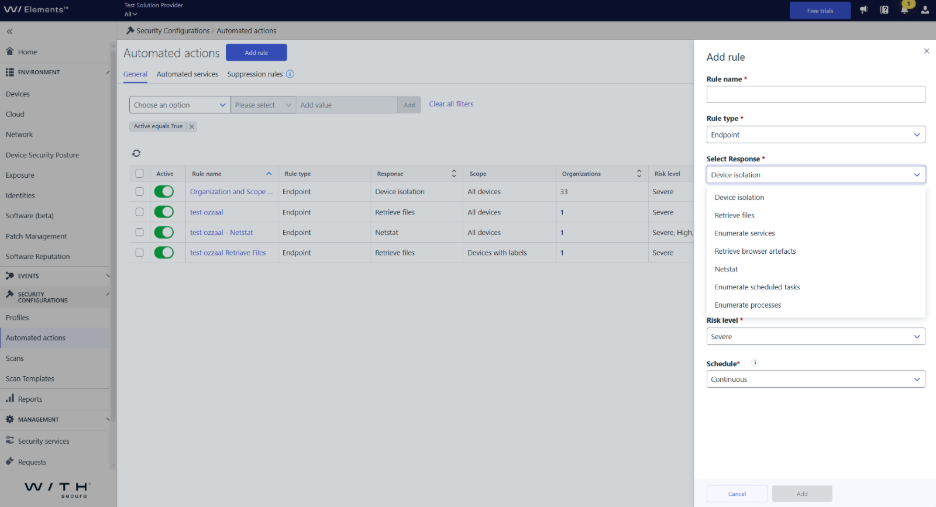
How rules work
When creating a rule with one of the new response actions, you choose a risk level trigger (Medium, High, or Severe) and a device scope. Rules set to “All Devices” can span multiple customer organisations; rules scoped to “Devices with specific labels” apply to a single organisation only. Schedule options remain Continuous or Custom, and the rule type is fixed to Endpoint. As with existing rules, the rule type and response type cannot be changed after creation, all other fields remain editable.
With automated EDR response actions, you can:
- Reduce manual effort when responding to endpoint threats,
- Ensure consistent, policy-driven responses to similar risk levels,
- Scale security operations across many customer organisations,
- Focus expert attention on complex investigations rather than repetitive tasks.
We believe this improvement will meaningfully reduce the manual burden on partners managing high volumes of endpoint detections, and bring the power of EDR response actions into your automated workflows.
-
Endpoint Security (formerly Endpoint Detection & Response) – 2026-06-29 Update
Read more
Dear community,
We are expanding the suppression rule capabilities in Elements EDR to give you greater control over large, complex detections. With this update, you can now suppress key detections individually from BCD Details – directly from the Timeline, Process tree, or Process details views.
What is changing?
Previously, the Accepted Behavior closure wizard was limited to BCDs with up to five unsuppressed key detections. This limit exists intentionally to keep auto-generated rule sets small, precise, and easy to audit. Raising it could produce unwieldy or overly permissive rules.
With this update:
- For BCDs with more than five key detections, you can now suppress each remaining detection individually after closing the BCD as Accepted Behavior.
- A new per-detection suppression option is available directly in the BCD Details view (Timeline, Process tree, and Process details tabs) for all BCDs closed as Accepted Behavior.
Three-level organizational hierarchy
Suppression rules follow a three-level organizational hierarchy: Company, SEP (Service Partner), and SOP (Solution Provider). Each level can independently create its own suppression rule for the same key detection, with a maximum of one rule per level. A rule created at a given level can only be edited by administrators at that same level or above – when editing is not permitted at your level, the Edit button is disabled and a tooltip explains who can modify the rule.
What does this mean for you?
- For large BCDs with more than five key detections, you no longer need to work around the detection limit – you can suppress the remaining detections individually after closure.
- You retain full precision – each suppression rule is still tied to a specific key detection and pre-populated from its context, keeping rules targeted and auditable.
- The existing Accepted Behavior wizard for BCDs with five or fewer key detections is unchanged.
We believe this improvement will significantly enhance the day-to-day experience of security teams managing large, complex detections, and make the suppression workflow more flexible without compromising precision or auditability.
-
Endpoint Security (formerly Endpoint Detection & Response) – 2026-06-26 Update
Read more
Dear community,
We are expanding device isolation capabilities in WithSecure Elements to now include Linux devices. Security administrators can remotely isolate a Linux device directly from the Elements Security Center when a security incident is detected, bringing Linux in line with the isolation functionality already available for Windows and macOS.
What is changing?
Device isolation has been available for Windows and macOS devices for some time, allowing administrators to contain active threats by restricting network communication while keeping the device visible and manageable in the Security Center. With this update, the same capability is now extended to Linux.
When a Linux device is isolated, its network communication is restricted to help contain active threats, prevent lateral movement, and limit potential impact during investigation and remediation. Isolation can be triggered as a response action from the Devices view and released once the incident has been resolved.
We believe this improvement will meaningfully strengthen your ability to respond to threats across mixed-OS environments, giving your security teams consistent containment capabilities whether the device in question is running Windows, macOS, or Linux.
-
Agent for Windows and Server – 2026-06-23 Update
Read more
A new version of the endpoint clients is available and our Early access program participants will start seeing it starting on 23.06.2026. Full availability will begin within the next week and takes some days to reach all customers.
This release makes the Elements Agent version 26.3 available (internal version 26.3.298).
The endpoints automatically upgrade, without a reboot.
This release introduces new features
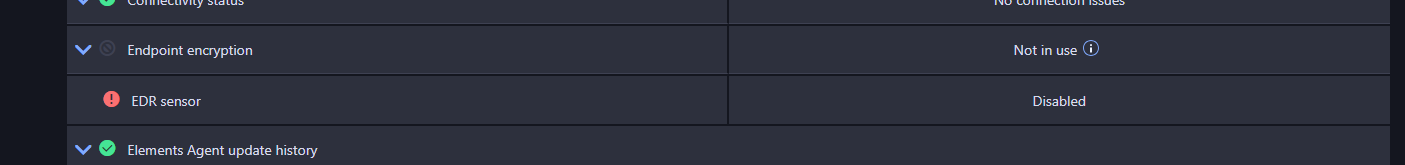
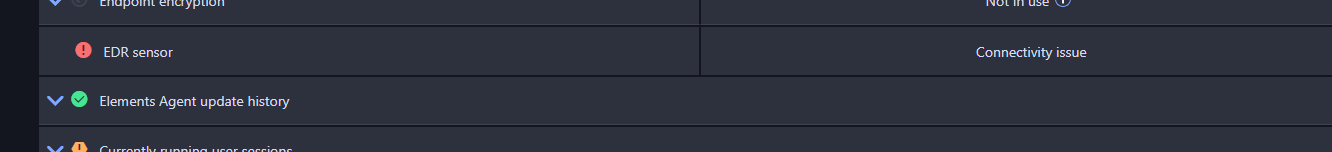
- Sensor Status Reporting : Elements Security Center can now report detailed Windows Sensor health states – enabled, disabled, connectivity issue, malfunction, or not applicable – giving users clearer visibility into Sensor issues beyond basic connectivity.


- Global Proxy State: The Windows Elements Agent now implements a shared proxy discovery mechanism, so all components reuse the first successfully discovered proxy rather than discovering independently – reducing delays in profile assignments and remote operations.
- Browser Extensions icon in the Settings sidebar is now visible in dark mode.